What are the main security risks in connected IoT devices and how to mitigate them?
Susana Oviedo
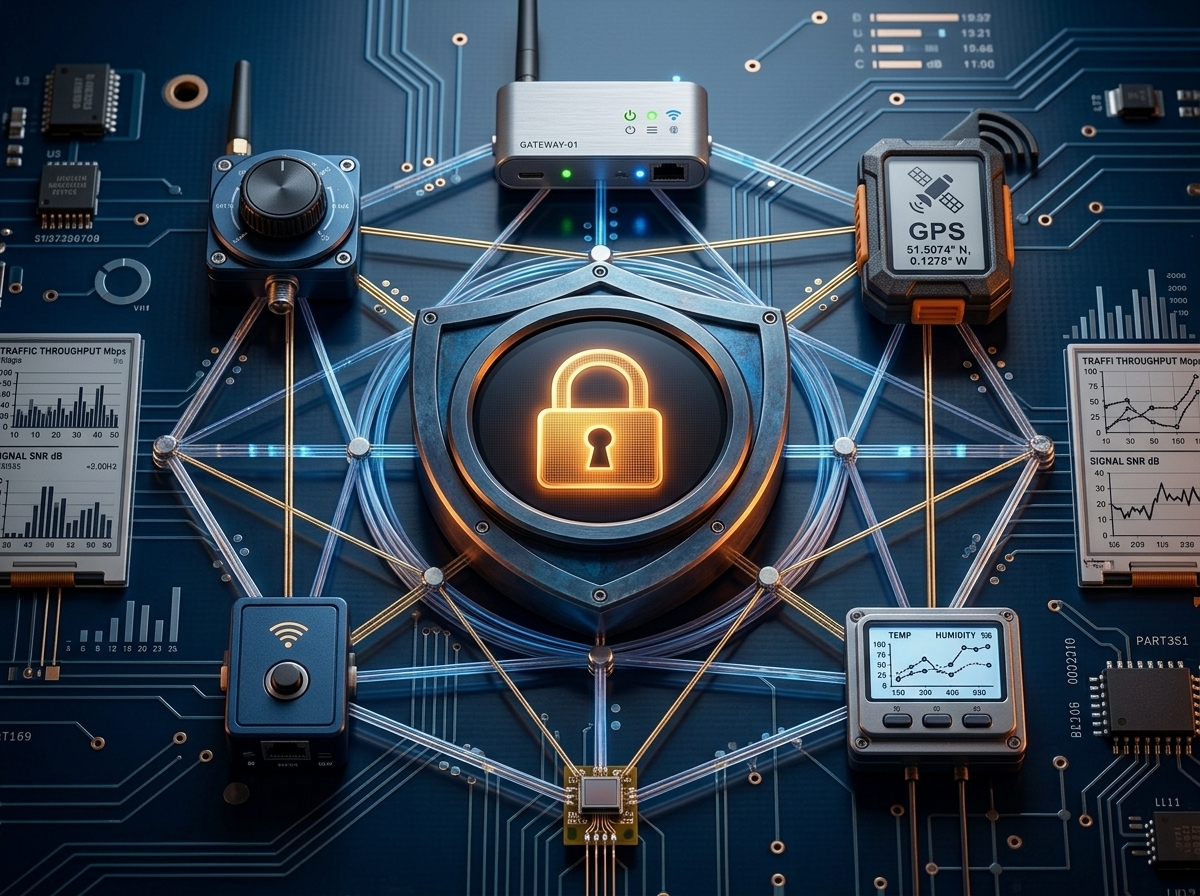
TL;DR: Connected IoT devices in enterprise networks face three critical threats: unchanged factory credentials, unencrypted communications, and the absence of per-device authentication. Mitigating them requires certificate-based authentication, network segmentation, in-transit encryption, and continuous monitoring of each device's behavior. In LATAM, where many deployments run over public or shared networks, these controls are not optional. They are the difference between a secure deployment and an open attack vector.
When a company deploys hundreds or thousands of IoT devices: meters, GPS trackers, industrial sensors, telemetry equipment. Each device is, technically, an entry point into the network. Most attacks against IoT infrastructure don't exploit sophisticated vulnerabilities: they exploit poor configurations that nobody had time to review.
This article explains the main security gaps in connected IoT fleets and the controls that technical teams should have in place before scaling.
Why are IoT devices a frequent target of attacks?
The answer is simple: they have low visibility and a long lifespan.
A corporate router is updated and audited frequently. An IoT sensor installed in a truck or on a light pole can go three years without anyone checking whether its firmware is up to date, whether it is still using factory credentials, or whether its SIM has traffic destination restrictions.
According to industry data, more than 57% of IoT devices are vulnerable to medium- or high-severity attacks, and the most common vector remains weak or non-existent authentication. In LATAM, where deployments typically rely on mixed network infrastructure: local operators, roaming, public APNs. The attack surface widens.
What are the most common vulnerabilities in enterprise IoT fleets?
1. Unchanged factory credentials. Many devices ship with default usernames and passwords that are never modified. These values are public. They're in the manufacturer's manuals, and scanning bots try them systematically. A fleet of 500 devices with factory credentials is 500 open doors.
2. Unencrypted communications. Protocols like HTTP, Telnet, or MQTT without TLS transmit data in plain text. On shared mobile networks or in roaming environments, this exposes both operational data and the device's control commands.
3. Outdated firmware. Without a remote update mechanism (OTA (Over The Air)), devices accumulate known vulnerabilities that never get patched. The problem worsens in geographically dispersed fleets where physical access to the hardware is expensive or impossible.
4. Lack of network segmentation. When all IoT devices share a network with corporate systems, a compromised device can become a pivot point to access critical infrastructure. Microsegmentation, isolating IoT devices on their own segment, is one of the highest cost/impact measures.
5. No behavioral monitoring. Without a behavioral baseline per device, it's impossible to detect anomalies: a device that suddenly starts generating three times the traffic or connecting to unknown destinations may have been compromised for weeks without anyone noticing.
Talk to a connectivity expert
From multioperador global coverage to a single management platform, we keep your devices connected everywhere.
Get in touchWhich security controls are priority for an IoT fleet?
Order matters. These are the highest-impact measures, sorted by implementation feasibility:
Certificate-based authentication (not passwords). Every device should have a unique identity, an X.509 certificate or equivalent, that authenticates it with the backend. If a device is compromised or replaced, the certificate is revoked without affecting the rest of the fleet.
Private APN or connectivity segmentation. Using a private APN instead of a public one means device traffic travels over a dedicated channel and doesn't pass through the open internet. This drastically reduces exposure to network attacks. Combined with traffic destination restrictions (IP whitelisting), it limits the blast radius of any compromise. Orion Private & Dedicated Network implements this model with a private network and dedicated VPN over multi-operator connectivity.
End-to-end encryption. TLS for all communications. If the device doesn't support TLS due to hardware constraints, evaluate alternative protocols like DTLS for UDP or implement application-layer encryption.
Centralized lifecycle management. Real-time visibility into each device's state: installed firmware, data consumption, last connection, traffic destinations. Is the foundation of any reactive security strategy. Without that visibility, incident response becomes slow and reactive.
OTA update policy. A defined process to distribute firmware updates remotely, with rollback capability and integrity verification, eliminates the technical debt accumulated in un-updated devices.
How does mobile connectivity affect IoT device security?
The SIM is the device's network identity. A SIM without configured restrictions can connect to any destination, use any roaming operator, and generate unlimited traffic. That is an attack surface that goes well beyond the device's software.
At minimum, security teams should require:
- Authorized APN restriction (the SIM can only use the corporate APN). - Destination IP whitelisting (the device can only communicate with defined servers). - Real-time anomalous consumption alerts (not end-of-month billing). - Immediate per-SIM blocking capability from a centralized platform.
These capabilities don't depend on the device's hardware. They depend on how the SIM is configured and what tools the team has to manage it.
In summary
IoT fleet security is not a one-time project. It's an operational discipline. The most frequent attacks don't exploit zero-day vulnerabilities: they exploit configurations nobody reviewed because "the device works fine". The right question is not "are we secure?" but "do we have the visibility to know?"
At Moabits, the Orion platform lets you manage each SIM's lifecycle with granular control: APN restrictions, consumption alerts, real-time blocking, and per-device traffic visibility. Combined with sound authentication and network segmentation practices, it's the foundation on which a secure IoT fleet is built at scale in LATAM.
Want to review the security configuration of your IoT fleet? Tell us how it's deployed today and we'll explore the missing controls together.
About Moabits
Founded in Spain in 2020, Moabits simplifies global IoT connectivity for companies that build, deploy, or resell connected solutions.
Through global SIM and eSIM coverage, smart automation, and our powerful platform Orion, we make managing connected devices seamless, so you can focus on scaling your business.
From service providers and MVNOs to OEMs and IoT solution developers, Moabits delivers the flexibility, visibility, and control needed to launch, manage, and grow smarter connectivity ecosystems worldwide.
Our Mission
Moabits empowers businesses to successfully deliver high quality connectivity services by providing a complete suite of solutions.
Our Vision
To provide technology to help connect the world, fostering global collaboration, enhancing efficiency, and improving the quality of life for all.
Let us look at your connectivity together
Whether you are scaling a fleet, deploying meters or launching a new IoT product, our team helps you choose the right coverage, plan and platform setup. Talk directly to the engineers and account managers who will run your project.
Get in touch